World
DHS data exposure: What is known about 41,000 records
DHS is investigating a potential breach affecting work-related personnel data; the claimed Okta route remains unproven.
What to know
- Reporters said a published collection contains work-related records associated with more than 41,000 DHS employees and contractors across the department and several components.
- DHS told WIRED it was aware of a potential breach and was actively addressing it; the agency had not publicly confirmed the attackers' claimed entry point when this article was prepared.
- The exposed fields reportedly include government contact and organizational information that could support phishing, impersonation or targeting when combined with other data.
- The group behind the release claimed the material came from a DHS Okta login environment, while Okta said it had no evidence that its own systems or data were compromised.
- NewsCubby has not downloaded, reproduced or linked to the exposed collection. Readers should not search for or redistribute it.
The Department of Homeland Security says it is addressing a potential breach after reporters examined a newly published collection containing work-related records tied to more than 41,000 DHS employees and contractors. The exposed material could help outsiders map parts of the department's workforce and contact staff, but the precise intrusion path and the full consequences remain under investigation.
WIRED and The Washington Post reported that the collection includes government email addresses, work telephone numbers, office information and internal organizational details connected to DHS headquarters and several components. A group calling itself the Department of Peace claimed responsibility and said the records came from a DHS identity-management environment using Okta. Okta said it had found no evidence that its own systems or data were compromised. That distinction is essential: public reporting has not established an Okta corporate breach.
What was reportedly exposed?
WIRED said it reviewed the material through Distributed Denial of Secrets, a transparency collective that received it from the group claiming responsibility. The records were reportedly current as of August 19, 2026, and covered more than 41,000 employees and contractors. The fields described in reporting are primarily work-related: agency email addresses, telephone numbers, office locations and organizational or group affiliations.
The scale makes the collection sensitive even if many individual fields resemble information that might appear in a directory. An internal directory gathers relationships in one place. It can show which people work together, which components employ contractors, how units are organized and which contacts may be useful for a convincing impersonation attempt. A malicious actor can combine that structure with other public or stolen information to build a more targeted message.
WIRED's analysis said roughly half of the records were associated with Customs and Border Protection, about 10,000 with Immigration and Customs Enforcement, about 6,200 with U.S. Citizenship and Immigration Services, and about 1,000 with the Cybersecurity and Infrastructure Security Agency. Those are reported estimates from the collection, not a final count certified by DHS. They may include contractors, duplicates, departed personnel or other records whose current status has not been independently confirmed.
This article intentionally does not identify employees, repeat internal group names, describe sensitive operational roles or provide a path to the material. The news value is the reported scope and security risk, not the republication of data that could increase harm.
Has DHS confirmed a breach?
DHS confirmed to WIRED that it was aware of a “potential breach” and was actively addressing the matter. That wording confirms an investigation and a response, but it stops short of validating every claim made by the group that released the data. DHS had not publicly explained the initial access method, the affected system, when access began, how long it lasted or whether all 41,000-plus records were authentic and current.
The Washington Post also reported on the appearance of the employee information online. Together, the two reports provide independent confirmation that a large collection was circulating and that DHS was examining the incident. They do not turn the attackers' technical narrative into an established fact.
In breach investigations, early numbers and labels often change. A forensic review may find that an account, a contractor environment, a tenant configuration, an exported directory or another system was involved. It may also narrow or expand the population affected. Until DHS publishes technical findings or a formal notification, the most accurate description is a reported personnel-data exposure and potential breach under active investigation.
NewsCubby readers can follow related security coverage in our report on emergency PHP security fixes, our explainer on AI agents being used in website attacks, and the AI and cybersecurity topic page.
Was Okta breached?
That has not been established. The group claimed that the records came from DHS's Okta single-sign-on environment. Okta is an identity and access-management company whose products can help organizations connect users to applications. A claim that data was taken from an organization's Okta environment is not automatically a claim that Okta's corporate infrastructure was penetrated.
Okta told WIRED it was aware of the report and had no evidence that Okta data or systems were compromised. Several scenarios could theoretically fit the limited public facts, including a compromised customer account, stolen session information, an abused administrative credential, an application connected to an identity directory or a separate export. Those are examples, not findings about this incident.
Attributing a breach requires logs, forensic evidence and access to the affected environment. The group has an incentive to portray its access as broad and consequential; the vendor and agency have incentives to be careful while investigating. Responsible reporting should preserve both statements and avoid filling the gap with speculation.
Why can work contact data create real risk?
Government email addresses and office numbers are not equivalent to Social Security numbers or bank records. But a structured directory can still be operationally valuable. An attacker who knows a person's agency, team, office and reporting relationships can create a message that sounds familiar. The message might impersonate a supervisor, help desk, contractor, benefits office or colleague and direct the recipient to a fake login page or malicious attachment.
The risk rises when directory information is combined with data from other breaches, professional profiles or social media. A work number can confirm that a target is active. A group affiliation can suggest what systems the person uses. Contractor labels can help an attacker mimic vendor communication. A list of colleagues can make a fraudulent request appear to be part of a normal project.
Some DHS components also employ people whose roles attract threats. That makes restraint especially important. Republishing a directory, searchable mirror or list of individuals can magnify the exposure even when the original purpose is commentary or transparency. Security researchers and journalists can report aggregate findings without turning their work into a discovery tool for harassers.
What did Bluesky do about links to the data?
In a late update, WIRED reported that Bluesky blocked links to a website hosting or searching the exposed material because the pages contained unauthorized contact information. The platform did not remove general discussion of the incident; it targeted links that provided access to the data.
That response illustrates the tension platforms face after a leak. Discussion about a government security failure can be newsworthy. Direct access to employee contact records can create privacy and safety risks. Blocking the distribution path while allowing reporting and commentary is one way to separate those interests.
The platform action does not authenticate every record or establish how the data was obtained. It does show that the practical effects extended beyond the initial release: services had to decide whether linking to the collection violated rules against exposing personal information.
What should readers avoid doing?
Do not search for, download, mirror, sort or republish the collection. Do not use it to contact employees, identify people in sensitive roles or test whether addresses and numbers work. Even apparently official data may be outdated, altered or mixed with inaccurate records. Redistributing it can increase harm and interfere with legitimate notification and investigation work.
Employees who believe they may be affected should follow official DHS and component security instructions rather than advice embedded in viral posts. Organizations should route suspicious messages through their established security teams. The public should be skeptical of urgent emails or calls that use accurate workplace details to demand passwords, codes, payments or document access.
NewsCubby does not have firsthand access to DHS systems and has not independently authenticated the dataset. Our account is based on named reporting, agency and vendor statements, and public platform actions.
What remains unknown?
The source of the initial access is not publicly confirmed. It is unknown whether the group penetrated a DHS-controlled tenant, obtained credentials from an individual, accessed a connected application, received an internal export from another person or used a different route. It is also unknown whether the exposure included fields beyond those described by reporters.
DHS has not publicly said how many records it considers valid, how many people it will notify, whether credentials were reset, whether systems were taken offline, or whether law enforcement has identified suspects. The reported August 19 date appears to describe when the records were last updated, not necessarily when an intrusion occurred.
There is also no public finding that Okta's own infrastructure was breached. Repeating the phrase “Okta breach” without qualification could wrongly assign responsibility and obscure other possibilities. The evidence supports saying that the attackers claimed an Okta-related source and that Okta disputes any compromise of its systems or data.
Why does the DHS exposure matter?
DHS combines immigration enforcement, border security, cybersecurity, disaster response, transportation security and other missions. A workforce directory spanning components can reveal relationships that are difficult to see from isolated public pages. That can help adversaries select targets, design social-engineering campaigns and infer organizational priorities.
The incident also tests the department's ability to communicate clearly. Employees need specific guidance, vendors need enough information to check their systems and the public needs a distinction between verified facts and attacker claims. Silence can create a vacuum, but premature technical conclusions can send defenders in the wrong direction.
The exposure is a reminder that identity systems are high-value infrastructure. Even when an attacker does not steal passwords, the surrounding directory can provide a map for the next attempt. Protecting identity environments involves access controls, phishing-resistant authentication, careful management of contractor accounts, monitoring of exports and prompt revocation when roles change.
What's next?
DHS's investigation should determine the access path, validate the affected records and decide whom to notify. The agency may release a formal incident notice, component-specific guidance or technical indicators. Okta may update its statement if forensic evidence points to a product issue or confirms that its systems were not involved.
Congressional committees and the DHS inspector general could seek briefings because the collection reportedly touches multiple components and sensitive workforces. Platforms may continue restricting direct links while allowing news coverage. Any revised count, confirmed intrusion method or evidence of misuse would be a significant update.
Until those findings arrive, the careful conclusion is limited: a large DHS-related personnel collection has been published; major outlets reviewed it; DHS is responding to a potential breach; the attackers' claimed Okta route remains unproven; and redistributing the data would create additional risk.
*Want more? Explore today's headlines on NewsCubby and join My Day free to make NewsCubby part of your day.*
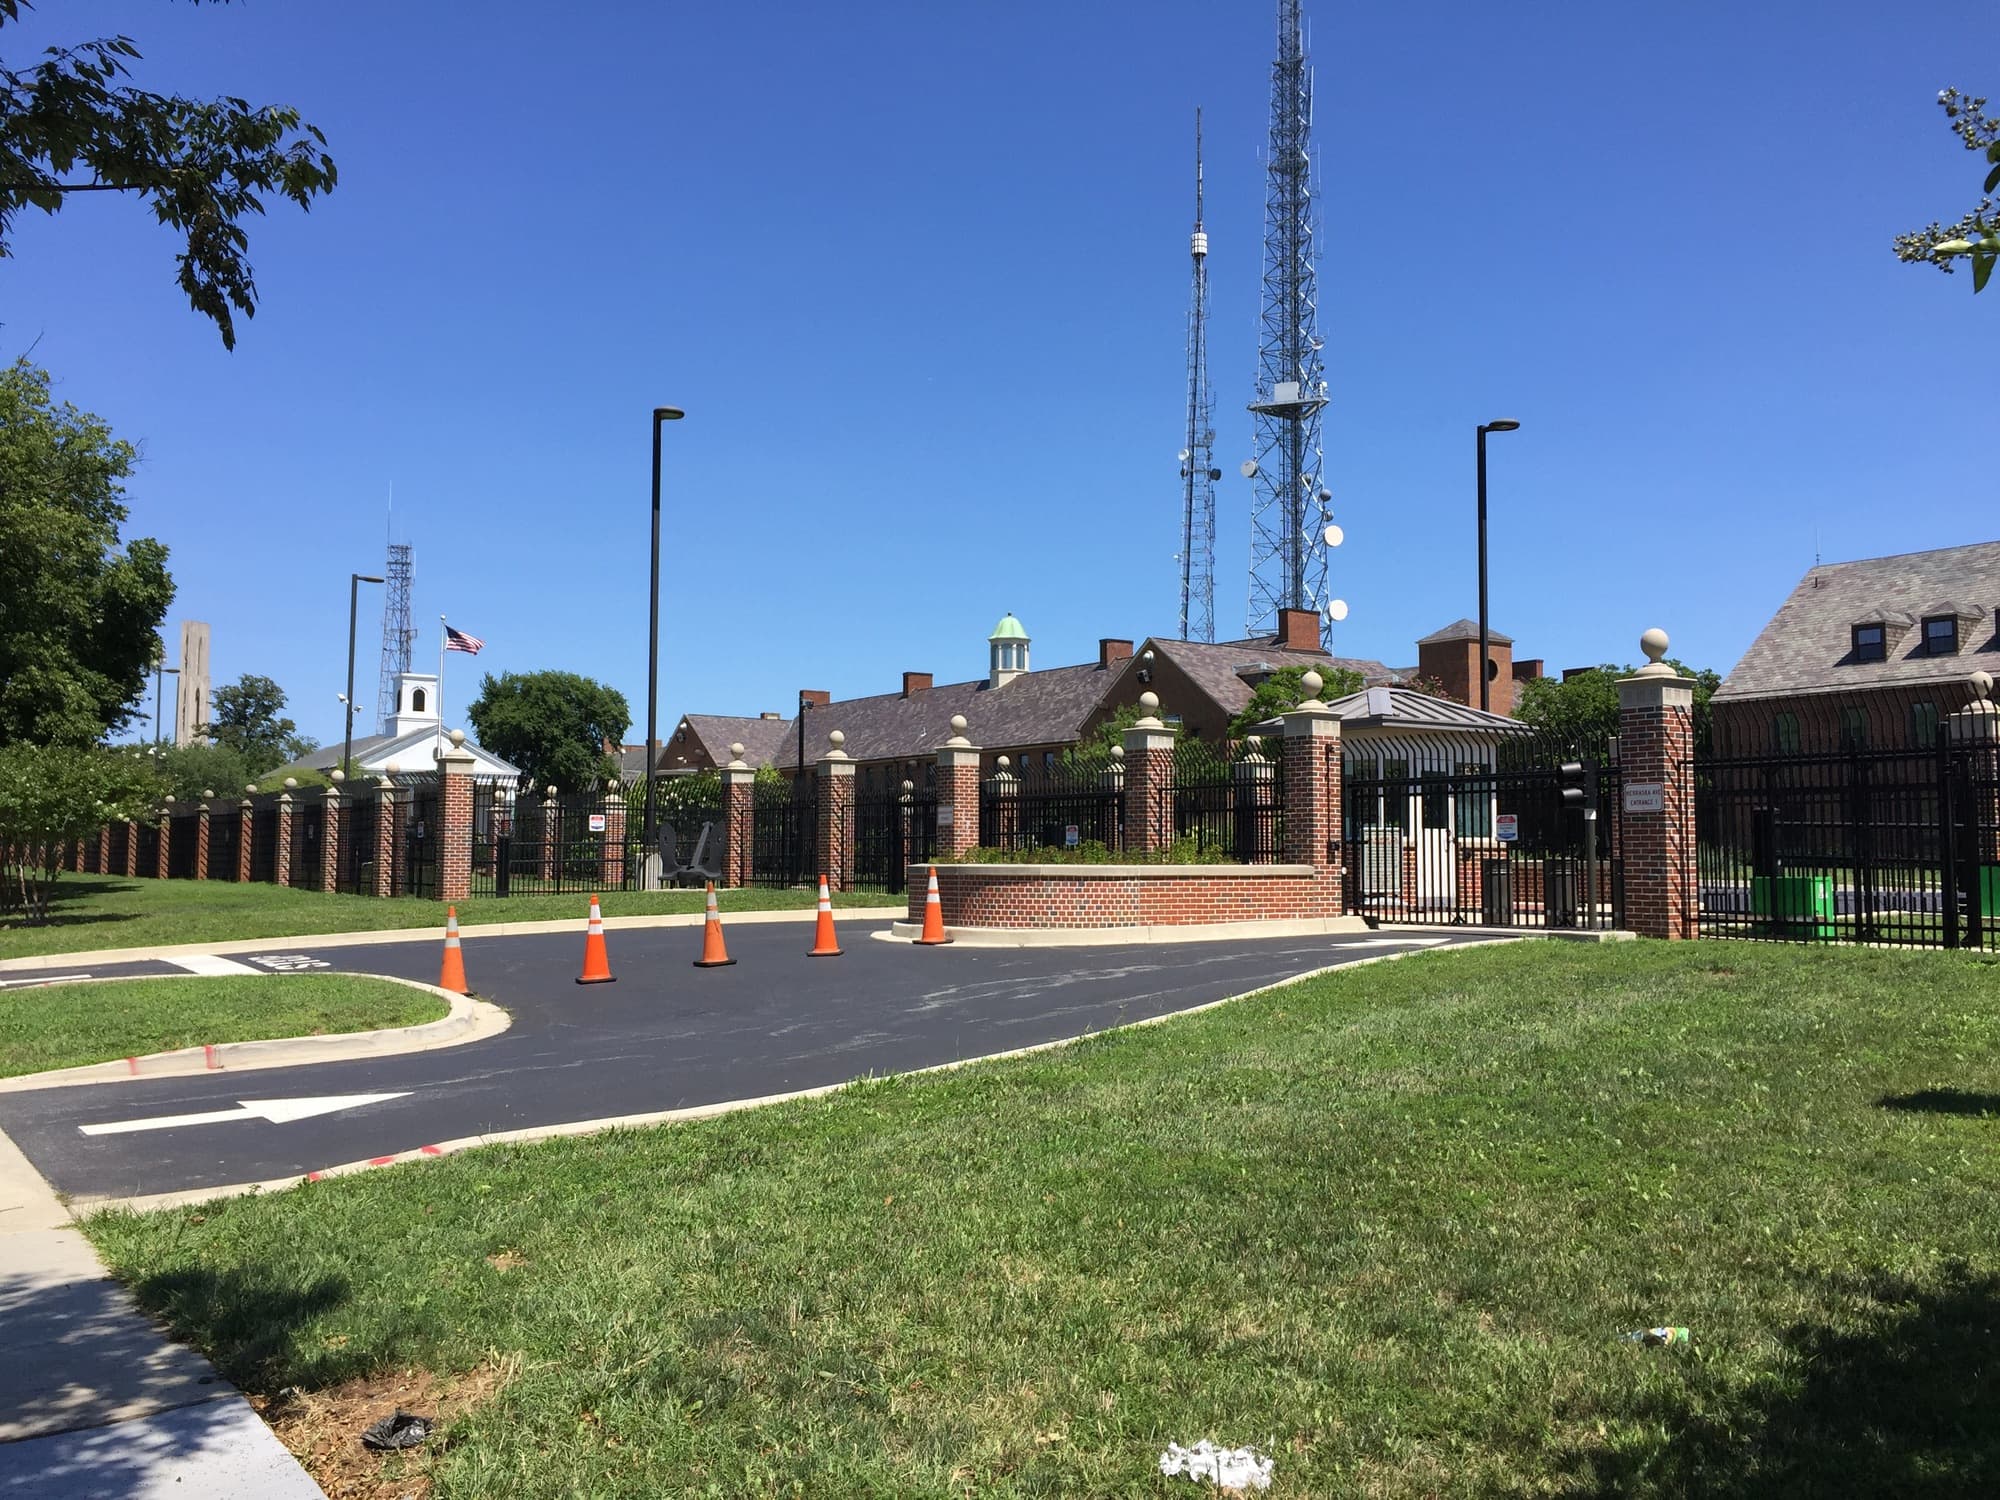
*ARCHIVE PHOTO: The Nebraska Avenue Complex in Washington, D.C., in 2017. Photo: Antony-22 / Wikimedia Commons / CC BY-SA 4.0.*
*This article was produced with AI assistance. Learn how NewsCubby uses AI.*